X-CAD · Open-source infrastructure
FRP SSH Guard
Open-source SSH access protection
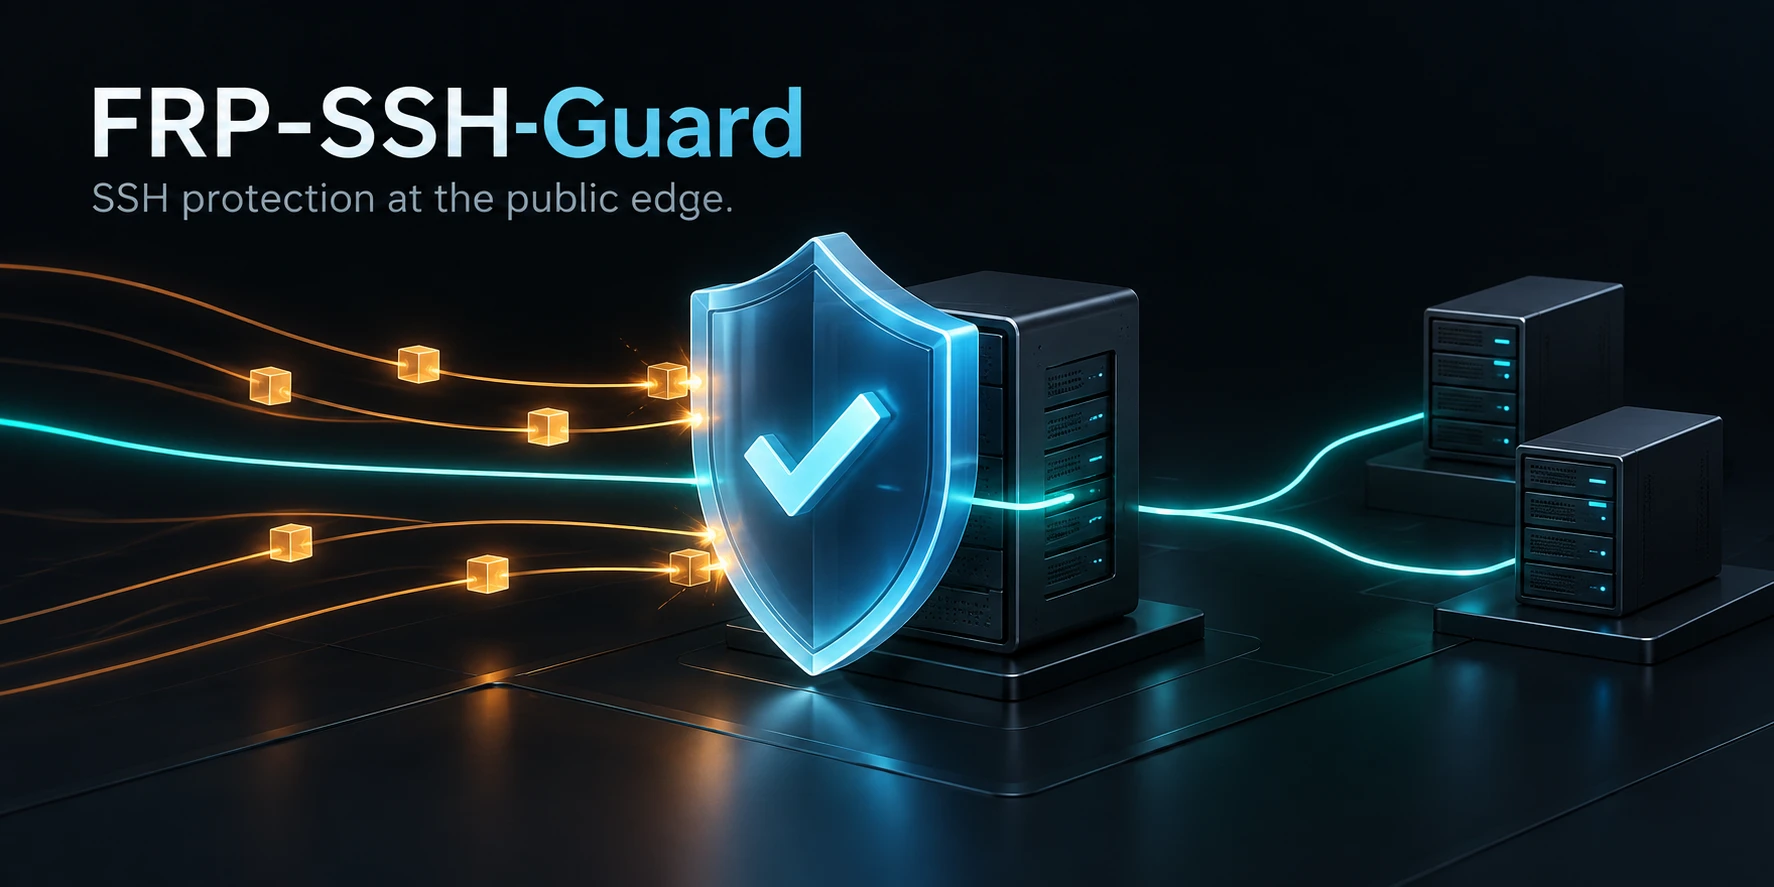
Protect FRP-forwarded SSH ports and your public server's own SSH service with connection limits, temporary bans, and access controls you can manage.
Why we built it
X-CAD runs behind FRP tunnels. Public SSH ports attract constant automated probes, and a forwarded port can quietly become the loudest door on the server. We wanted a small, explicit guard that lives on the public host and limits abuse before it reaches the private backend.
What it does
FRP-SSH-Guard adds an nftables policy for the ports you choose:
- Per-source, per-port new-connection rate limits and temporary source bans.
- A shared per-port limit to reduce distributed connection bursts.
- IPv4/IPv6 IP and CIDR allow/block lists, optionally scoped to selected ports.
- Ban history and longer bans for repeatedly observed offenders.
- Optional protection for local SSH port 22, including failed-authentication and invalid-user detection from the server’s sshd logs.
- Shared bans across protected ports or separate jails per port, plus permanent or timed manual blocks.
- Automatic trusted-source learning from successful administrator logins to the public host; it can be disabled with
LEARN_ADMINS=off. - Explicit activation, reboot restoration, and recovery of a missing guard table.
For forwarded SSH, the guard observes new TCP SYN packets; authentication results inside the encrypted tunnel remain unavailable. Local SSH monitoring reads the public server’s own sshd journal and never collects passwords. It complements SSH authentication and other firewall controls.
Download and install
Get the Debian package and checksum from the latest release. Use the installation instructions on that release page for the downloaded package, and follow the deployment guide to configure protection.
For upgrades, review the migration guide for changes to settings and behavior. An active guard refreshes during installation; fresh or disabled installations still require port selection and activation.
Editable settings and allow/block lists live in ~/.frp-ssh-guard/. Configuration changes require check and reload. Version-specific changes are covered in the release announcements below.
Observed deployment
An operator-reported snapshot from one deployment, October 13–17 2026, recorded:
- 3,206,432 dropped packets vs 967 passed — 99.97% of those counters.
- SSH connections reaching backends down from roughly 200/hour to 2 in the latest 60 minutes.
- Backend failed logins: 6,442 before the guard, 0 observed in the latest 24-hour window.
These are observations from one deployment, supplied by its operator. The exact deployed version and raw logs were not supplied for independent verification. Traffic, settings, and logging coverage affect results.
Open source
FRP-SSH-Guard is MIT licensed. The Debian package, source, tests, and bilingual documentation are available on GitHub. The release’s validation record lists tested platforms and remaining coverage limits.